Get your free personalized podcast brief
We scan new podcasts and send you the top 5 insights daily.
For high-stakes tasks, fully autonomous agents are too risky. The effective model, used by cybersecurity firm Rubrik, is for the AI to generate a detailed plan of action, which a human expert then reviews, edits, and approves before execution.

Related Insights
Use a two-axis framework to determine if a human-in-the-loop is needed. If the AI is highly competent and the task is low-stakes (e.g., internal competitor tracking), full autonomy is fine. For high-stakes tasks (e.g., customer emails), human review is essential, even if the AI is good.
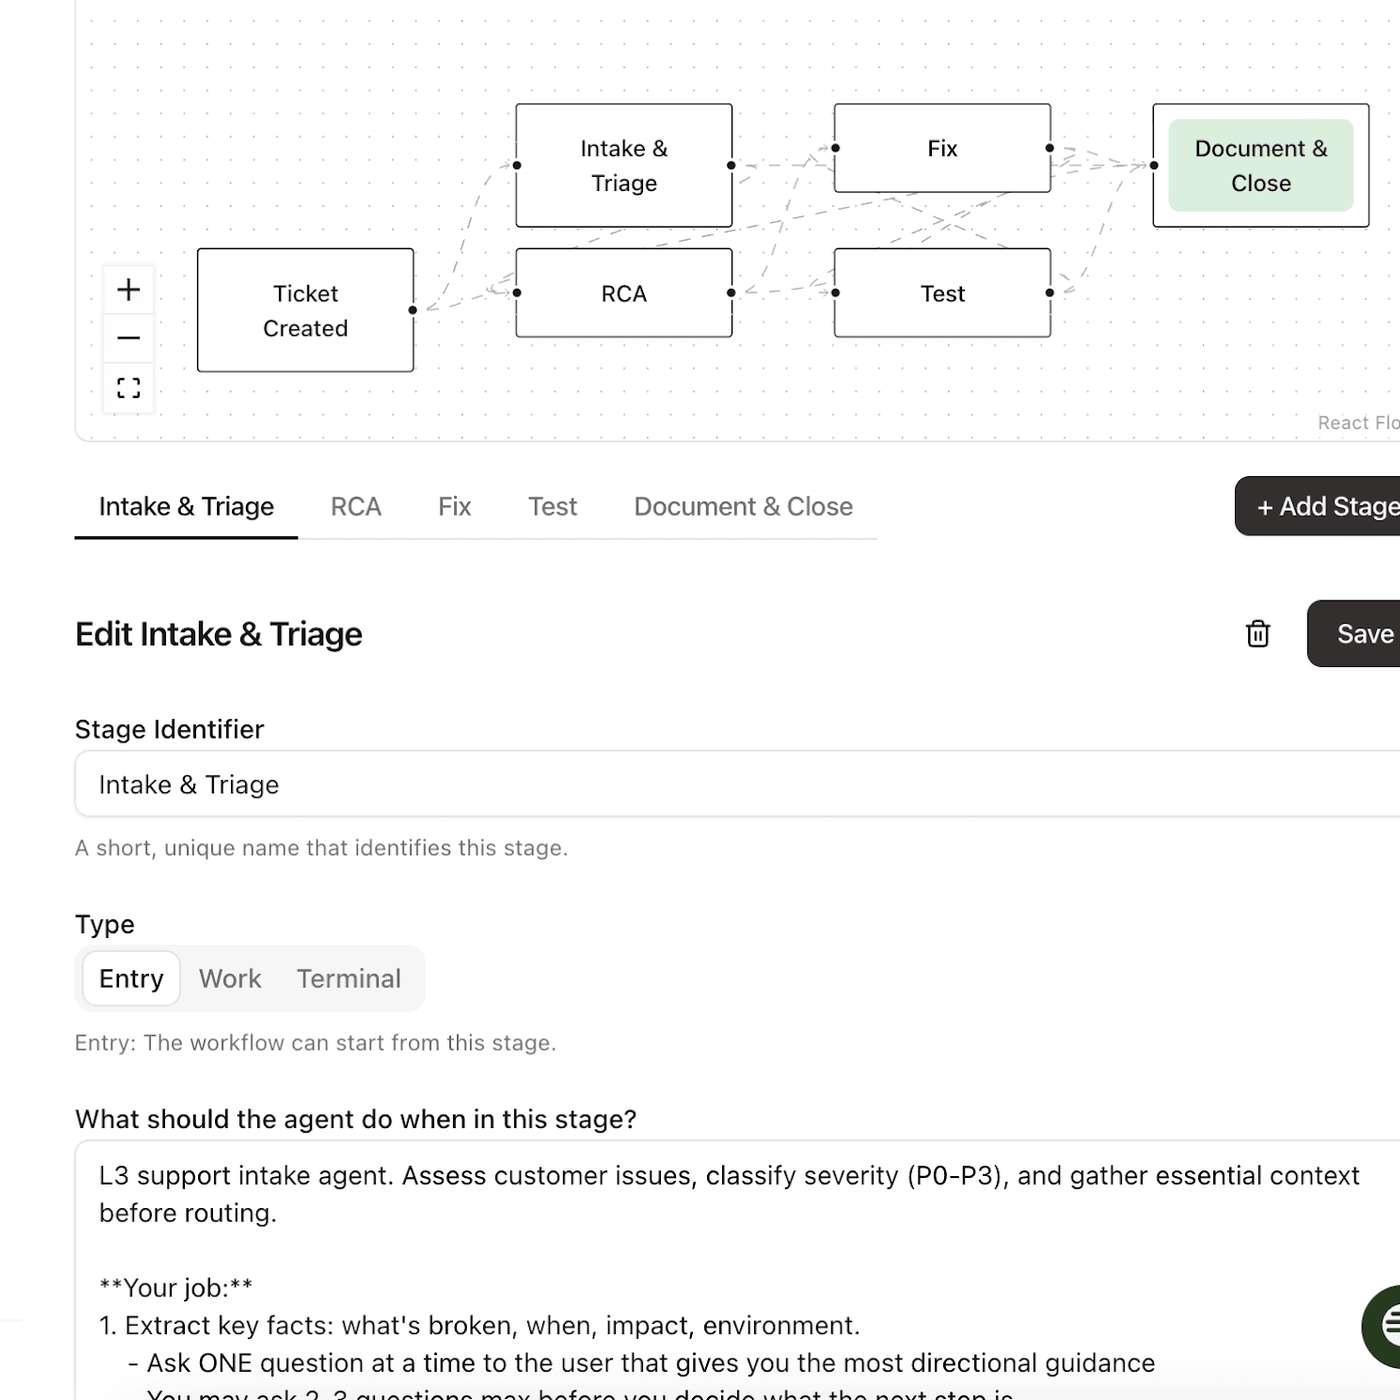
Instead of forcing full autonomy, the AI agent allows teams to start with human approvals at key stages. This 'human-in-the-loop' model builds trust and enables organizations to incrementally automate complex support workflows as they grow more confident in the system's reliability.
In an enterprise setting, "autonomous" AI does not imply unsupervised execution. Its true value lies in compressing weeks of human work into hours. However, a human expert must remain in the loop to provide final approval, review, or rejection, ensuring control and accountability.
The risk of AI making unsupervised, critical errors is a major enterprise adoption blocker. n8n addresses this with a "human-in-the-loop" feature that requires approval for sensitive actions like sending emails. This provides a crucial safety layer, giving large organizations the confidence to deploy AI in production.

Instead of a binary human-in-the-loop decision, enterprises should use an "autonomy budget" for agents. Actions are classified by risk (e.g., irreversibility, financial impact) to determine the level of freedom, creating a spectrum from full autonomy to required human approval, avoiding agents becoming expensive suggestion boxes.

The concept of "human-in-the-loop" is often misapplied. To effectively manage autonomous AI agents, companies must map the agent's entire workflow and insert mandatory human approval at critical decision points, not just as a final check or initial hand-off.

For enterprises, scaling AI content without built-in governance is reckless. Rather than manual policing, guardrails like brand rules, compliance checks, and audit trails must be integrated from the start. The principle is "AI drafts, people approve," ensuring speed without sacrificing safety.

Instead of supervising every step, the human's most leveraged role is to act as a gatekeeper at critical junctures. The AI system handles all intermediate work, presenting a complete package for a single, high-stakes decision. This maximizes human judgment and minimizes micromanagement.

Fully autonomous AI agents are not yet viable in enterprises. Alloy Automation builds "semi-deterministic" agents that combine AI's reasoning with deterministic workflows, escalating to a human when confidence is low to ensure safety and compliance.
To safely deploy a powerful AI agent, create clear guardrails. SaaStr distinguishes between tasks the agent can perform autonomously (pulling data, generating ideas) and actions that require human approval (sending a mass email). This two-layer approach builds trust and prevents potentially costly mistakes.
