Get your free personalized podcast brief
We scan new podcasts and send you the top 5 insights daily.
BeReal's U.S. Managing Director proposes a simple architectural solution to combat AI-generated deepfakes: disable uploads from the camera roll. Forcing in-app content capture ensures authenticity in a way that watermarks or detection algorithms cannot.

Related Insights
As AI models improve, detecting AI-generated content will become increasingly difficult. A more sustainable long-term strategy may be to focus on verifying and labeling authentic, camera-captured content. This flips the problem from an arms race of detection to a system of verification.
Adam Mosseri’s public statement that we can no longer assume photos or videos are real marks a pivotal shift. He suggests moving from a default of trust to a default of skepticism, effectively admitting platforms have lost the war on deepfakes and placing the burden of verification on users.
A simple method to detect a common type of real-time deepfake is to ask the person to place their fingers in front of their face. While the AI can generate realistic hands held separately, the complexity of overlaying them on the face often causes the model to glitch and break the illusion, providing a practical, low-tech verification test.
Politician Alex Boris argues that expecting humans to spot increasingly sophisticated deepfakes is a losing battle. The real solution is a universal metadata standard (like C2PA) that cryptographically proves if content is real or AI-generated, making unverified content inherently suspect, much like an unsecure HTTP website today.

The shift from "Copyright" to "Content Detection" in YouTube Studio is a strategic response to AI. The platform is moving beyond protecting just video assets to safeguarding a creator's entire digital identity—their face and voice. This preemptively addresses the rising threat of deepfakes and unauthorized AI-generated content.
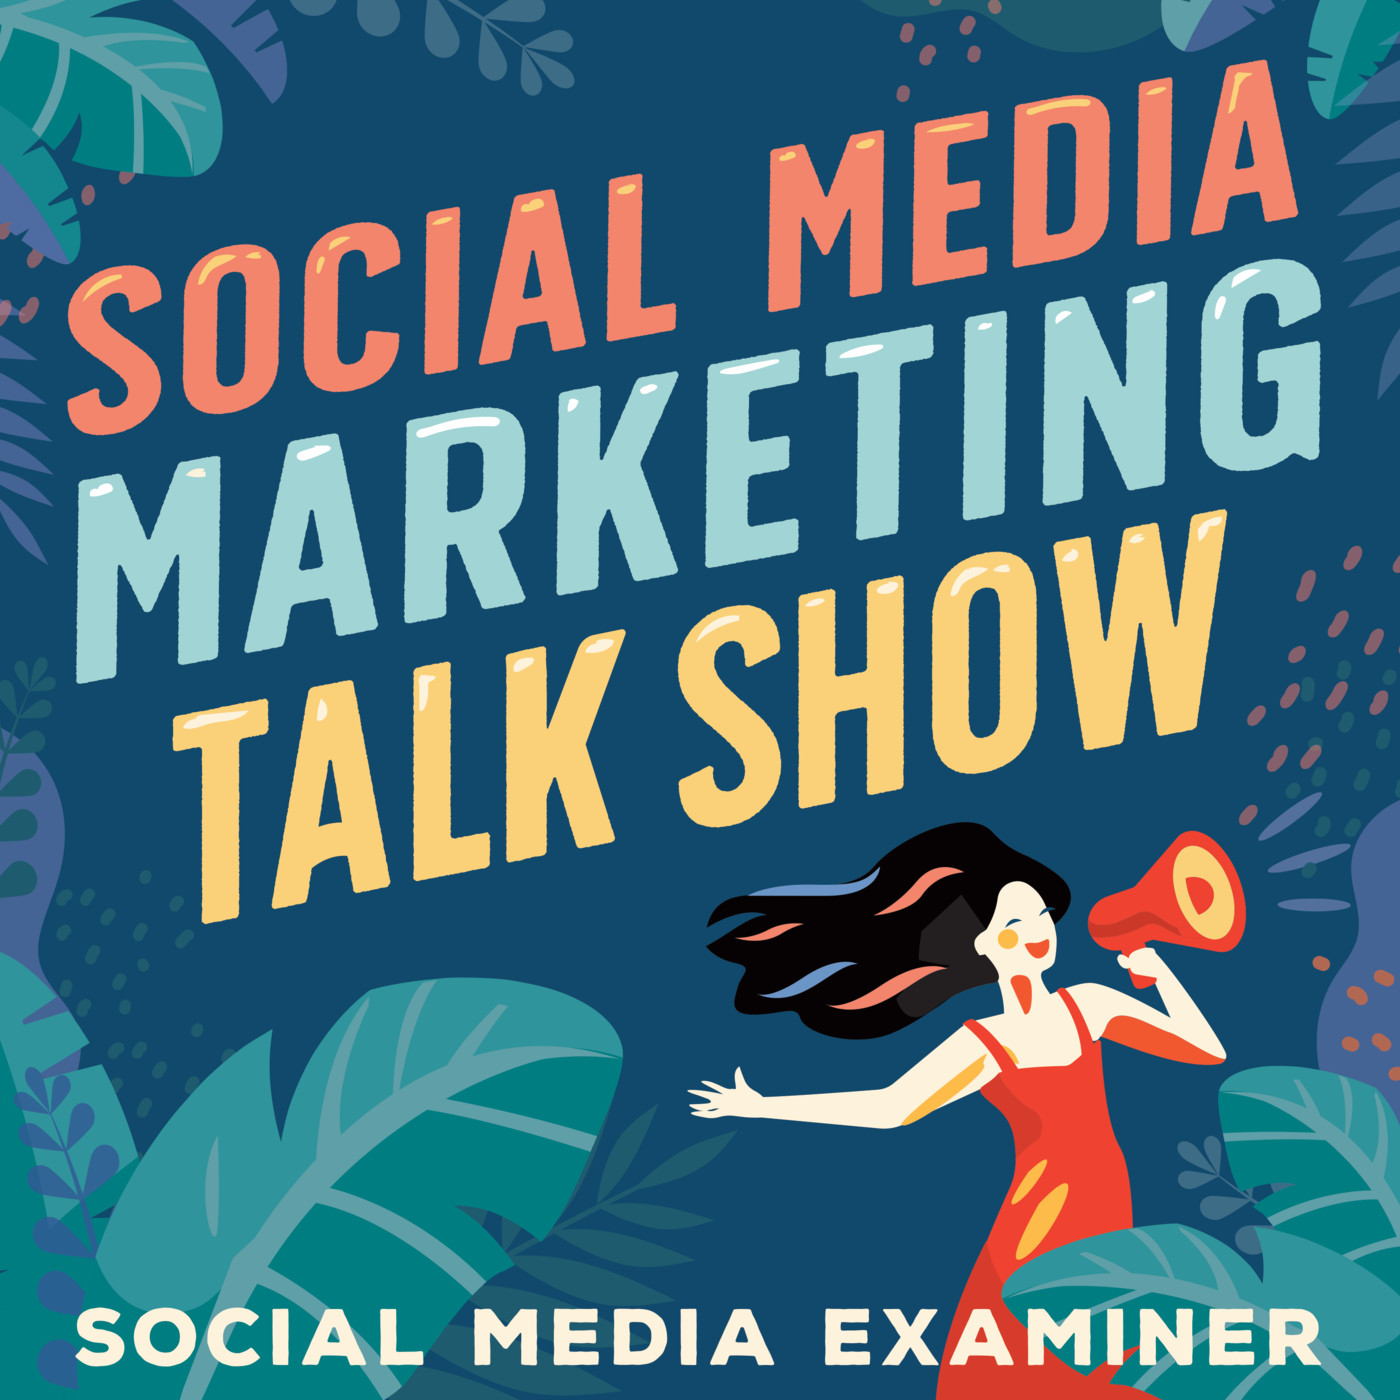
Instead of detecting AI fakes, a new approach focuses on proving authenticity at the source. Organizations like C2PA work with hardware makers to embed cryptographic signatures into photos and videos, creating a verifiable chain of "content provenance" that proves an asset was captured by a real device.
OpenAI provides a free image verification tool. Marketers can use this tool to their advantage by uploading their edited, ChatGPT-created images. This allows them to confirm that their modifications successfully removed detectable AI fingerprints before publishing the content.
Cryptographically signing media doesn't solve deepfakes because the vulnerability shifts to the user. Attackers use phishing tactics with nearly identical public keys or domains (a "Sybil problem") to trick human perception. The core issue is human error, not a lack of a technical solution.

Initiatives like Google's Synth ID aim to standardize detection of AI-generated content. However, these systems are vulnerable. Simple user actions like screenshotting can strip metadata, and blending AI-generated assets with real footage can easily confuse detection algorithms, limiting their effectiveness.
Current responses to deepfakes are insufficient. Detection is an endless cat-and-mouse game with high error rates. Watermarking can be compromised. Provenance systems struggle with explainability for complex media edits. None provide the categorical confidence needed to solve the crisis of digital trust.
