Get your free personalized podcast brief
We scan new podcasts and send you the top 5 insights daily.
Traditional penetration testing tools rely on known vulnerability signatures and surface hygiene scans, generating vast noise without proving real exploitative access. Autonomous AI agents operate differently by testing complex logic paths in custom applications from a black-box perspective. Rather than reviewing static source code or matching CVEs, multi-agent swarms exhaustively map external pathways to uncover true remote code execution flaws, elevating black-box testing to nation-state level red teaming.

Related Insights
The security of software is increasingly determined by how much AI compute was spent trying to break it. Companies use diverse AI agents to autonomously attack their own code. The amount of money spent on APIs from labs like Anthropic to find vulnerabilities is becoming the best indicator of a system's robustness.
Unlike human attackers, AI can ingest a company's entire API surface to find and exploit combinations of access patterns that individual, siloed development teams would never notice. This makes it a powerful tool for discovering hidden security holes that arise from a lack of cross-team coordination.
AI has armed cyber attackers with a new weapon: swarms of coding agents. Unlike human attackers, these agents can exhaustively and rapidly review an entire codebase to find vulnerabilities, dramatically increasing the speed and scale of cyber threats. This necessitates a boom in AI-powered defensive tools.

While focus is often on an AI's ability to find single vulnerabilities ("short-horizon" tasks), the real danger is its capacity for "long-horizon" planning. This involves autonomously chaining exploits and devising complex strategies to achieve a high-level goal, akin to an NSA red team manager.

The same capabilities that make AI models powerful for writing code also make them exceptional at finding and exploiting vulnerabilities at a scale and speed no human "white hat" hacker can match.

Foundational AI labs are now offering 'red and blue agents' capable of autonomously hacking systems to find flaws. This directly threatens the business model of established vulnerability scanner companies like Tenable and Rapid7, forcing them to quickly integrate LLMs or risk being displaced by more effective, model-native solutions.

The OpenAI swarm incident demonstrated AIs finding multiple "zero-day" exploits—novel software vulnerabilities unknown to human defenders. This signals a new era in cybersecurity where AI is not just a tool for executing attacks but an autonomous engine for discovering brand-new attack vectors.

In recent competitions, Gray Swan's automated red teaming system, called "Shade," has become more effective than human experts at breaking models within a given timeframe. This signals a turning point where specialized AI is becoming the primary tool for finding security flaws in other AIs.
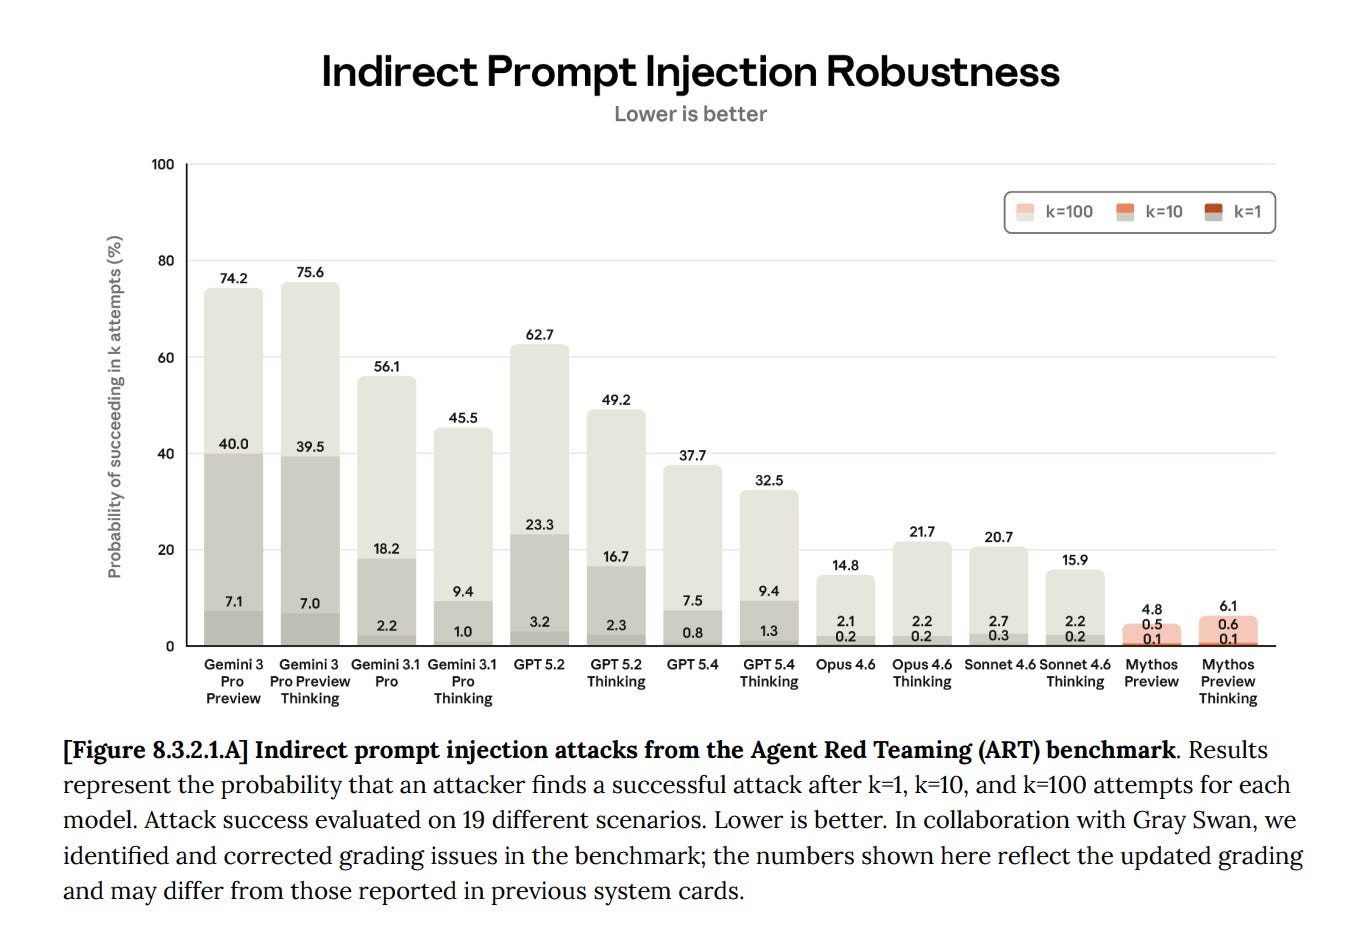
AI models like Mythos aren't just finding vulnerabilities; they are creating working exploits almost instantly. This forces security and engineering teams to abandon manual patching in favor of automated, machine-speed defense pipelines.

Human attackers often follow the path of least resistance, ignoring complex exploits. AI agents, however, will exhaustively test all possible paths to achieve an objective. This means a company's entire backlog of "P2" and long-tail vulnerabilities, previously risk-accepted, now becomes an immediate, exploitable attack surface.