Get your free personalized podcast brief
We scan new podcasts and send you the top 5 insights daily.
Ben Sabrin found that forcing enterprises to reconstruct existing identity infrastructure kills agent adoption immediately. Instead of introducing foreign policy languages, architectures must ingest current sources of truth like database entitlement systems, SailPoint, or Entra ID, acting as an ambient policy enforcement point across existing enterprise access rules.
Related Insights
While individuals can experiment with agents on laptops, true enterprise adoption is impossible in that model. Corporate security, reliability, and collaboration demands require moving agents into a formal, distributed environment with proper tooling and guardrails. This marks the necessary shift from a personal productivity tool to a core, team-based business process.

Enterprises will not adopt multi-agent AI without two non-negotiable conditions. First, effective guardrails must be in place to ensure safety and compliance. Second, systems must be interoperable, as enterprises will inevitably use agents from diverse vendors like Salesforce, Microsoft, and Google, not a single provider.

Traditional identity models like SAML and OAuth are insufficient for agents. Agent access must be hyper-ephemeral and contextual, granted dynamically based on a specific task. Instead of static roles, agents need temporary permissions to access specific resources only for the duration of an approved task.

Adopting a comprehensive AI identity model can be done in phases. First, register agents as governable actors with stable identities and roles. Later, add runtime instance linkage and detailed context lineage. This incremental path provides immediate and significant governance gains without requiring a complete overhaul of identity systems from day one.

Ben Sabrin notes that placing authorization guardrails inside language models fails because models break internal boundaries to achieve their goals. Instead, platforms like Arcade act as deterministic external policy enforcement points. They inspect and strip credentials before tools ever execute or reach the language model.
The conversation around Agentic AI has matured beyond abstract policies. The consensus among consultancies, tech firms, and academics is that effective governance requires embedding controls, like access management and validation, directly into the system's architecture as a core design principle.
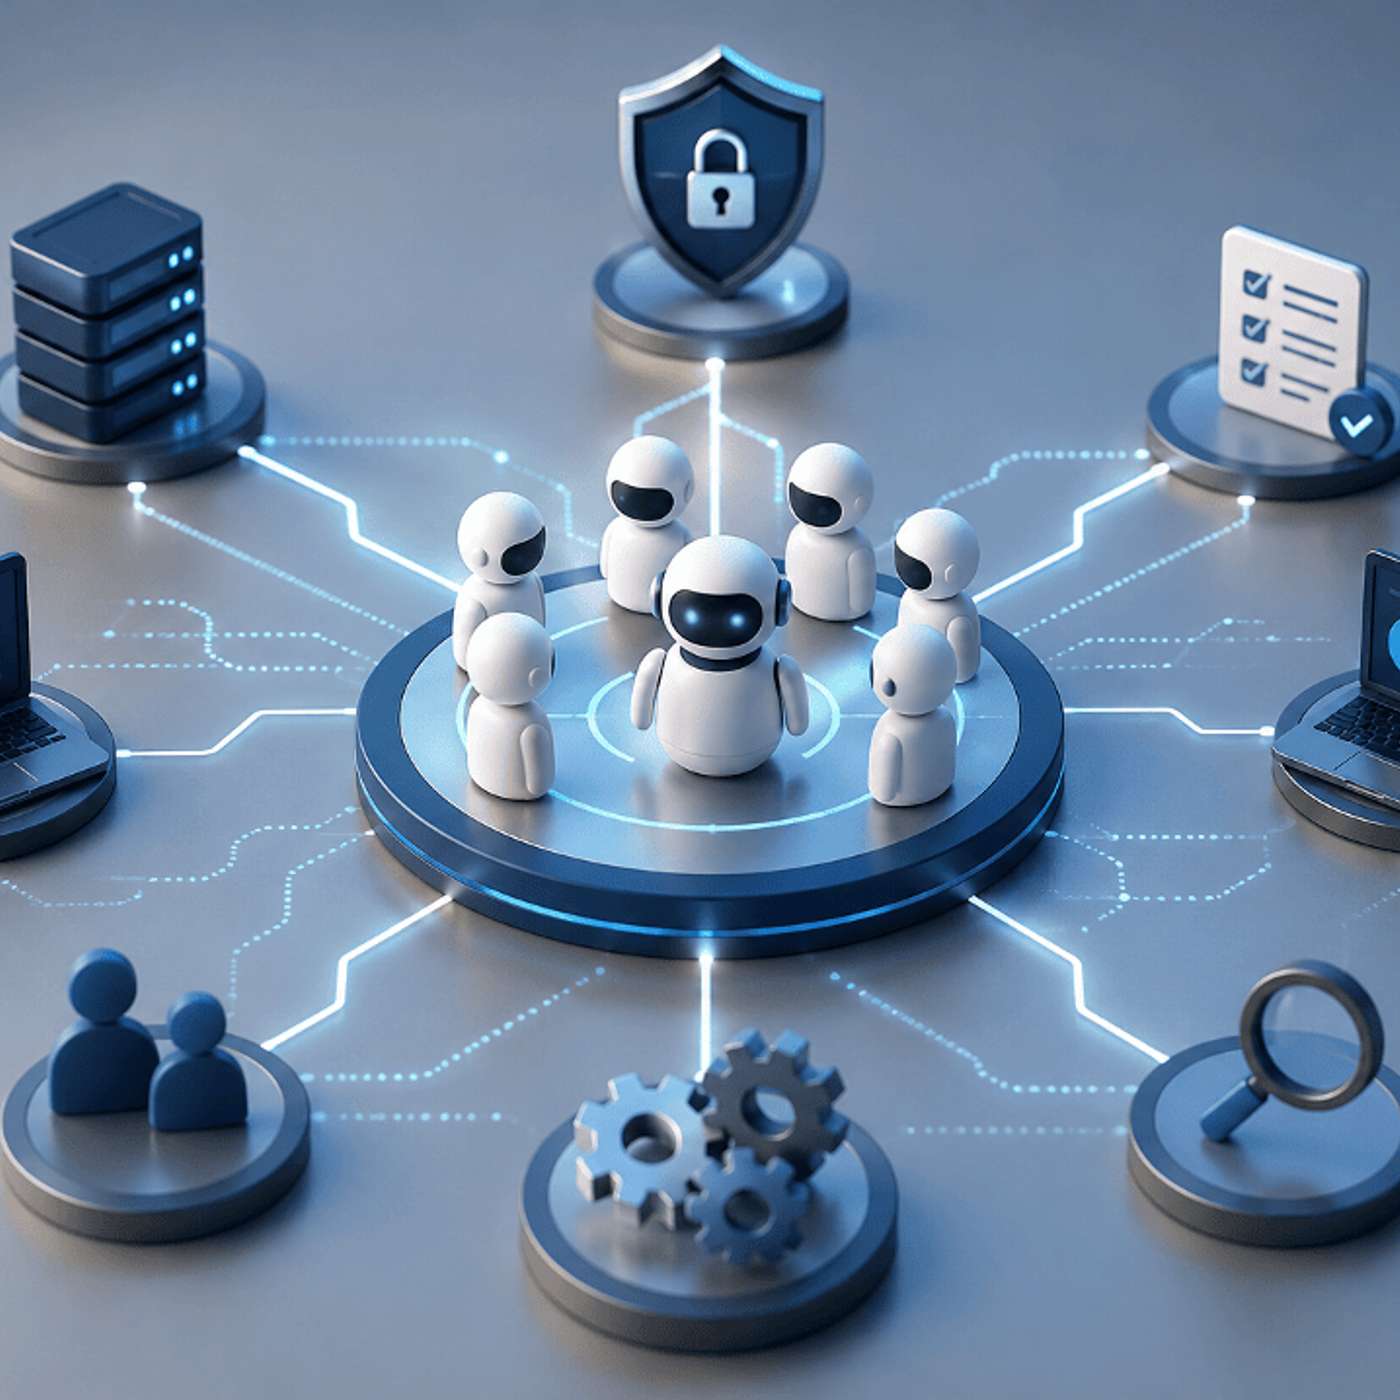
A single AI agent can provide personalized and secure responses by dynamically adopting the data access permissions of the person querying it. This ensures users only see data they are authorized to view, maintaining granular governance without separate agent instances.
For AI agents to move beyond human oversight, they'll need their own identities, budgets, and authorization to consume services. This creates a new enterprise tooling category focused on agent governance, ensuring they don't "run wild" with resources or access sensitive data.

The primary barrier to enterprise AI agent adoption isn't the AI's intelligence, but the company's messy data infrastructure. An agent is like a new employee with no tribal knowledge; if it can't find the authoritative source of truth across siloed systems, it will be ineffective and unreliable.

Instead of building complex new control layers for AI, the emerging best practice is to treat each agent as a separate entity. This means giving them their own accounts, API keys, and permissions, mirroring how you would onboard a new human employee to manage access and security.