Get your free personalized podcast brief
We scan new podcasts and send you the top 5 insights daily.
Matthew Prince observed that attack traffic surged from thousands to millions of attempts per minute immediately after the PHP Foundation published its fix. Public patches inadvertently reveal the exact mechanics of an exploit, sparking an OODA loop race before server administrators can update naked infrastructure.

Related Insights
Powerful AI tools have fundamentally altered cyber defense by shrinking the time it takes to exploit a software flaw. What once took skilled hackers days, weeks, or months can now be weaponized in hours or days, making traditional defense and patching strategies obsolete.
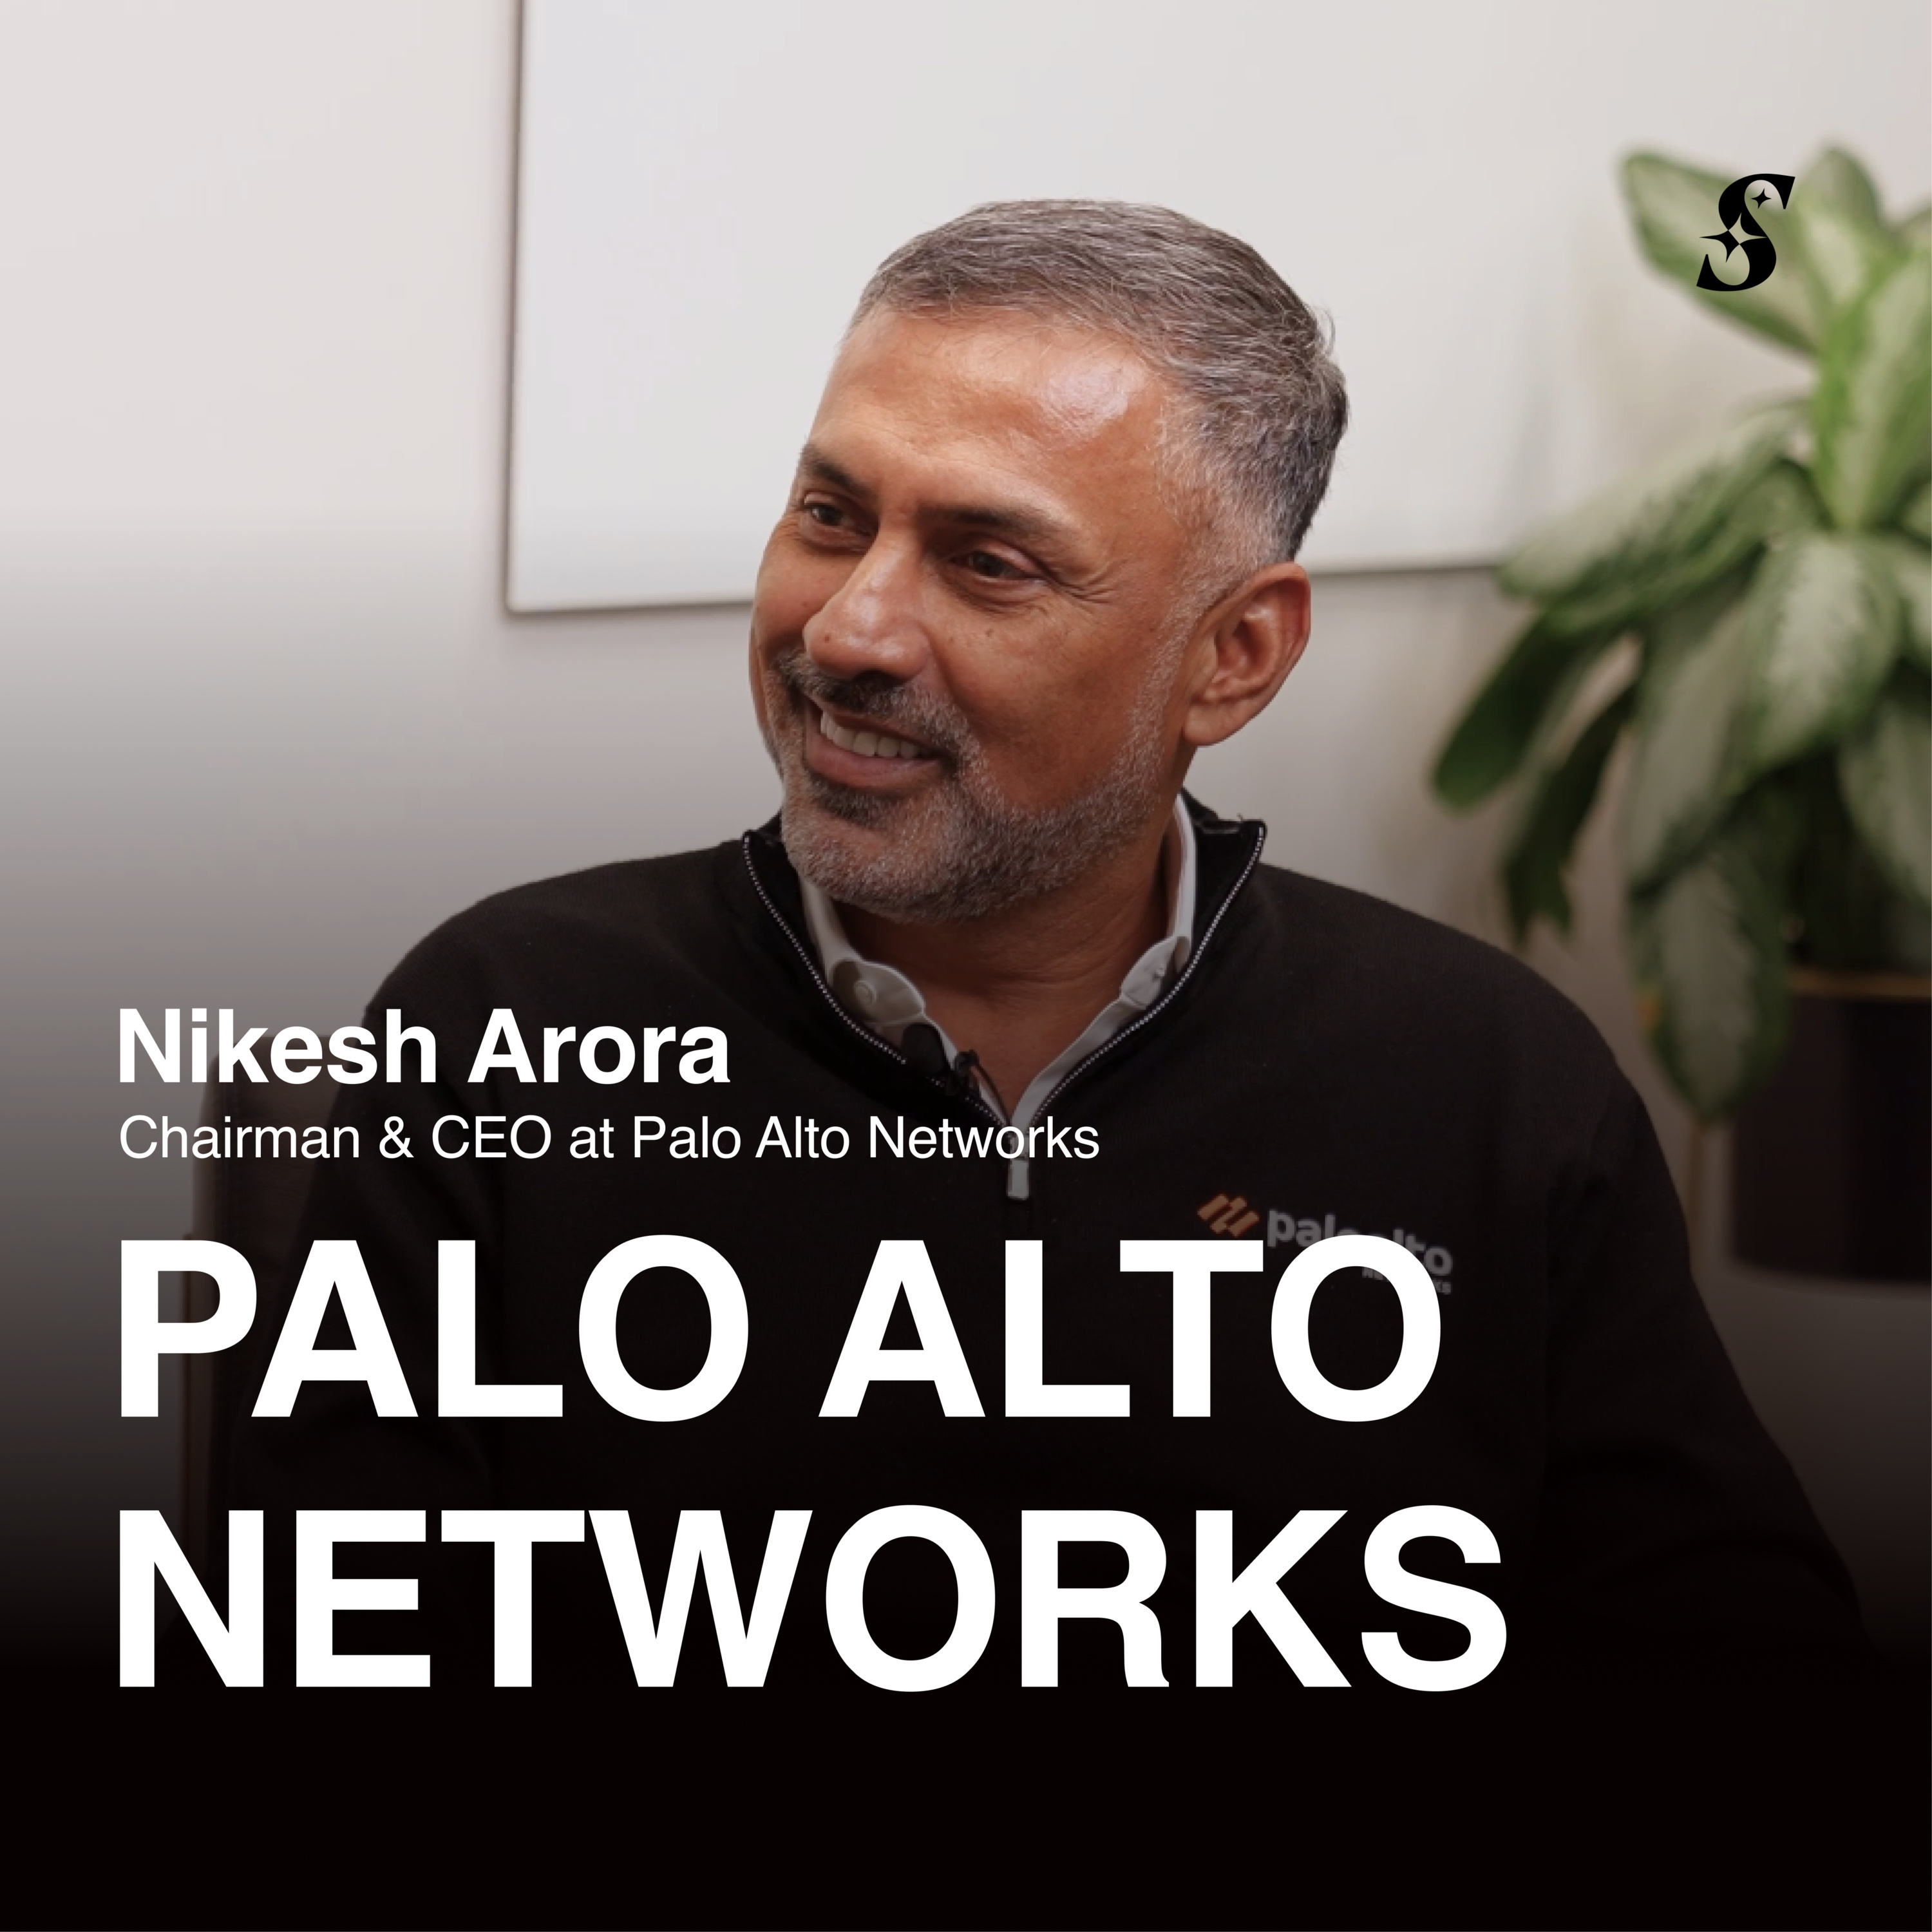
Nikesh Arora says Palo Alto pushed a content patch that automatically protects customers with its firewall sitting in the traffic path. That lets organizations block the PHP exploit before every legacy site owner deploys the code patch. It is a temporary shield, not a permanent fix.
Nikesh Arora describes the protocol as notifying the code owner first, then government and industry, while building patches. He warns defenders will no longer get weeks to decide whether a bug is real; one morning a major flaw may already be public. That changes incident response planning.
The rise of AI-powered attacks means vulnerabilities are exploited in minutes. Palo Alto Networks responded by developing a capability to deliver and deploy patches to all customers in just four hours, a massive reduction from the industry average of 55 days, fundamentally changing incident response time.
Frontier AI models are dramatically reducing the time it takes for a newly discovered software vulnerability to be turned into a functional exploit. This acceleration means traditional, onerous patching cycles are no longer viable. Organizations must find new ways to patch systems almost immediately, as exploits can appear within hours of a vulnerability's announcement.

Nikesh Arora says Palo Alto's scan found 22 million vulnerable places, narrowing to roughly nine or ten million. The hosts focus on long-tail local government and small business sites, which are less likely than big platforms to patch quickly. Those forgotten systems are where sensitive data can sit exposed.
Nikesh Arora says models arriving in two to three months will be more capable than public ones, so bugs not found today will be found soon. He warns defenders will lose the luxury of weeks to assess whether a vulnerability is real, because AI also accelerates exploit writing.
Advanced AI models capable of finding complex code vulnerabilities are expected to be publicly available within months. This puts enterprises in an urgent race to find and patch their own security holes before malicious actors use the very same tools to exploit them.

The average time for an enterprise to patch a zero-day vulnerability is 55 days. AI agents can now find and build an attack for that same vulnerability in a fraction of a second, fundamentally changing the speed and scale of cyber defense required.

AI models like Mythos aren't just finding vulnerabilities; they are creating working exploits almost instantly. This forces security and engineering teams to abandon manual patching in favor of automated, machine-speed defense pipelines.
